Application Security Built for eCommerce

The plugin CVE you couldn't patch is how the skimmer got in.

Your biggest security risk isn't an unknown zero-day. It's a known CVE in a checkout plugin or platform you can't patch fast enough. Miggo is an Application Detection and Response (ADR) platform: it shows which vulnerabilities are actually exploitable in your checkout applications, and shields them at runtime while the patch waits.
Book a Demo
Start a 30-day trial of WAF Copilot + Runtime Sensor
Not ready to talk to sales? See how it works.

Trusted by Industry Leaders

Recognized by

It Already Happened

Magecart campaigns have run for years through known, unpatched Magento and Adobe Commerce CVEs. The attacker gets in through a public vulnerability with a patch available, then injects the skimmer. British Airways lost roughly 429,000 card records the same way in 2018 and drew a £20M ICO fine, reduced from an initially announced £183M. The vulnerability is public, the patch exists, and the window between the two is where the breach lives.

429,000

card records

20M

ICO fine

In three moves, mitigate the gap

No rearchitecting. No months-long deployment. Runtime protection that closes exploitable paths while your backlog runs.

1. Know

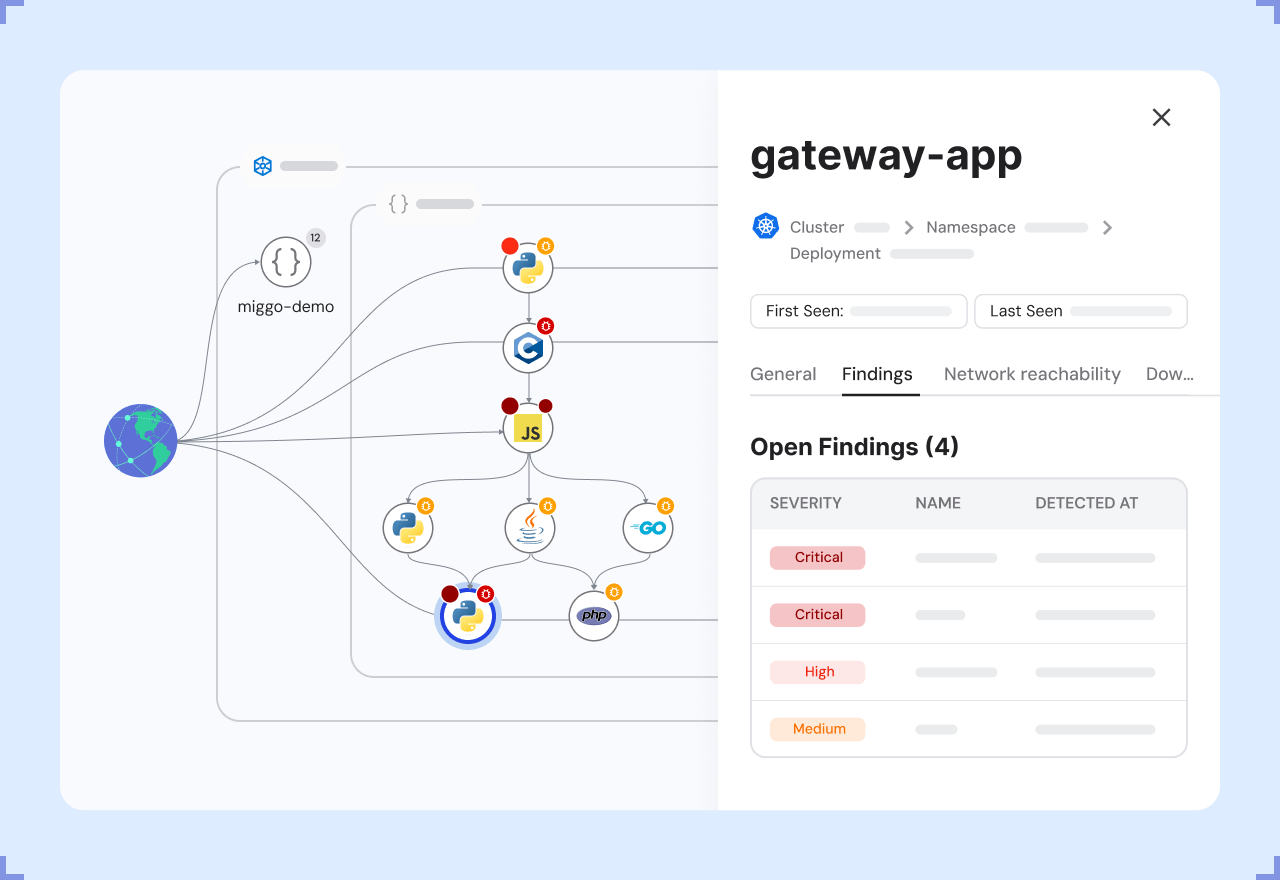
See your full runtime attack surface

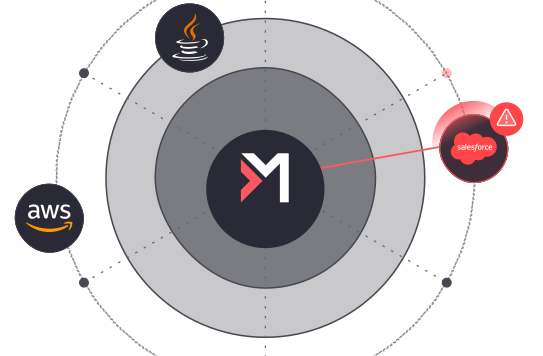
Miggo maps every live service, integration and data flow across your checkout environment, including platform plugins and payment integrations, without code changes.
Auto-discovered application graph
PCI cardholder data and loyalty PII flows tagged live
New plugins and integrations surfaced instantly
2. PROVE

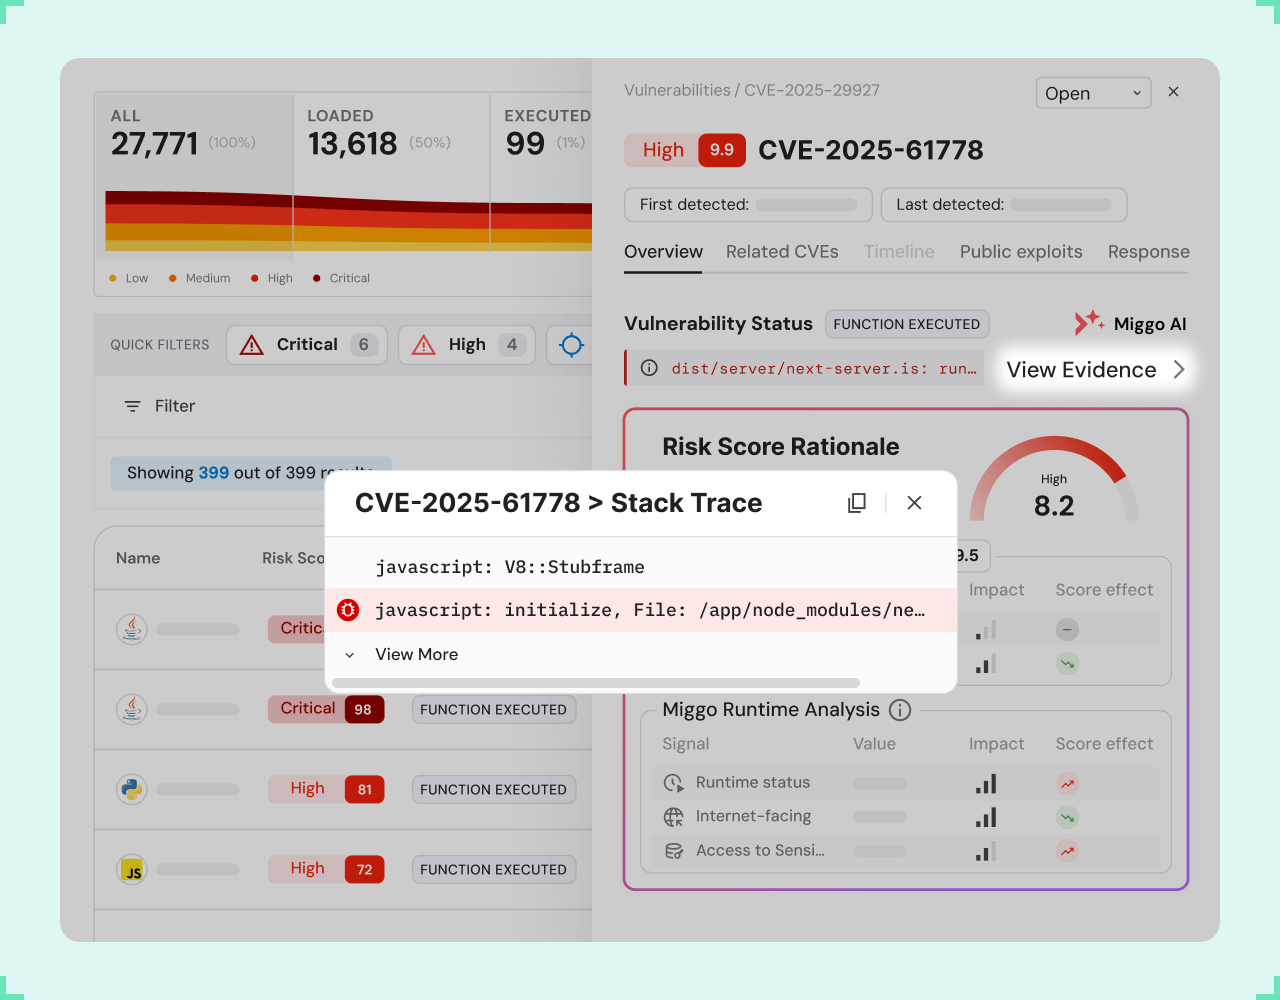
Prioritize what’s actually exploitable

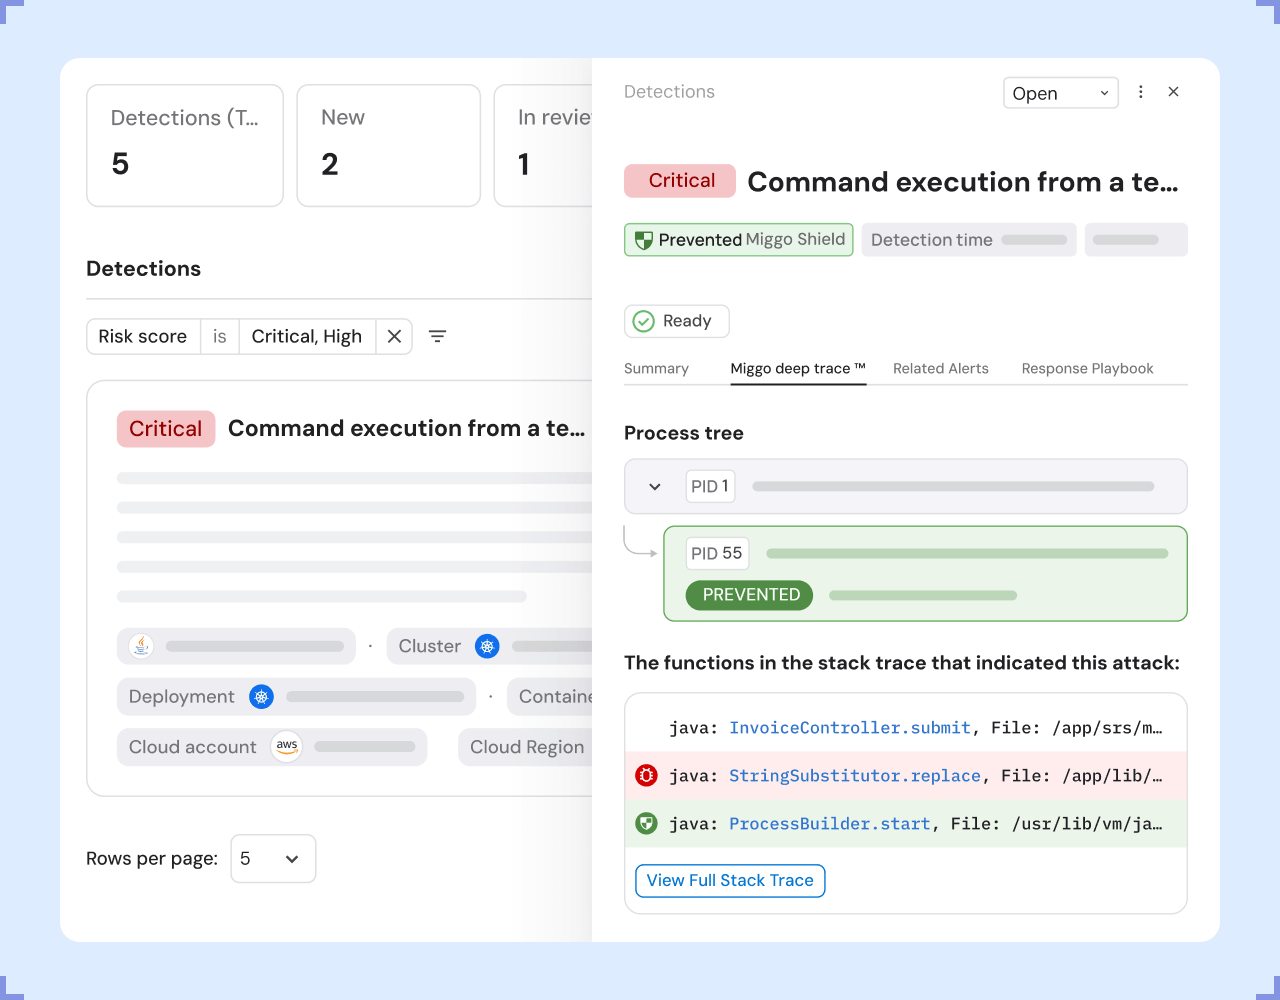
Vulnerability prioritization driven by runtime reachability, not by CVSS score. Filter your CVE backlog against your production checkout environment and stop pulling engineering off roadmap work for plugin vulnerabilities that can't be reached in prod.
Attack path visualization
PCI-ready risk context

3. SHIELD

Shield instantly with virtual patching

For every exploitable CVE in a checkout plugin or third-party integration you can't remove without breaking the purchase flow, Miggo generates a precise WAF rule, deployed in seconds, no code change required.
Auto-generated WAF rules per CVE
1-click deploy to AWS WAF & Cloudflare
Rules expire when patch ships

Want to see this run against your own environment?

Free, and you keep the report either way.

What customers get out of it

99%

of a typical CVE backlog is unreachable in production

50%+

less time spent assembling compliance and audit evidence

<1hr

to deploy the sensor, agentless and with no code changes

"Miggo's team felt like an extension of ours. In a moment of uncertainty, they jumped in, analysed live telemetry, and helped us rule out a potential threat in minutes."

Roye Jacobovich
VP R&D and CISO, Eitan Medical

Where Miggo Fits in Your Compliance Picture

Requirement What Miggo provides
PCI DSS v4.0 Req 6.4.3 Evidence of live request behavior and active exploit protection on your checkout applications.
PCI DSS v4.0 Req 11.6.1, script integrity Nothing. Miggo does not monitor client-side script integrity.
PCI DSS v4.0 Req 12.10 Runtime detection and attack-path evidence to support incident response.
Requirement:
PCI DSS v4.0 Req 6.4.3
What Miggo provides:
Evidence of live request behavior and active exploit protection on your checkout applications.
Requirement:
PCI DSS v4.0 Req 11.6.1, script integrity
What Miggo provides:
Nothing. Miggo does not monitor client-side script integrity.
Requirement:
PCI DSS v4.0 Req 12.10
What Miggo provides:
Runtime detection and attack-path evidence to support incident response.

See Your Gap. On Us.

Run a free backlog reality check against your production environment and see exactly where you’re exposed to cardholder data.

No credit card

No agent install

Results in minutes

Nothing to sign

Agentless eBPF-OTel sensor, deploys in under an hour

Frequently Asked Questions

Does Miggo stop Magecart or client-side skimming?

Not directly. Miggo closes the server-side door those campaigns come through: the known, unpatched platform and plugin CVEs that let an attacker inject in the first place. Magecart itself is client-side script skimming, a separate category; for script integrity monitoring under PCI DSS 11.6.1 you will need a dedicated control.

What can we do about a CVE in a checkout plugin we can't remove?

Miggo virtual-patches it. It generates a WAF rule scoped to the specific exploitable path and deploys it in seconds, so the plugin keeps running and the exploit path closes. The rule expires when the plugin patch ships.

How do you know which CVEs are actually exploitable in our platform?

Miggo maps your running checkout applications and tests each CVE against real runtime reachability rather than against a plugin inventory. Across Miggo deployments, roughly 99% of a CVE backlog turns out to be unreachable in production.

Does this help with PCI DSS 6.4.3?

Yes, and see the table above for what is and isn't covered. It also cuts the time spent assembling audit evidence by hand by more than 50%.

How long does deployment take, and will it affect checkout?

Under an hour, with no code changes and no impact on the purchase flow. Miggo uses an agentless eBPF-OTel sensor, so there is nothing to install in your storefront.