Oops! Something went wrong while submitting the form.
The Moat Was Scarcity: Part 2
AI erases the time between vulnerability discovery and exploitation. Defenders still have an advantage: Here’s how to turn that knowledge into protection before a patch lands.
Read More
Security
Latest Posts
0 results matching
tag
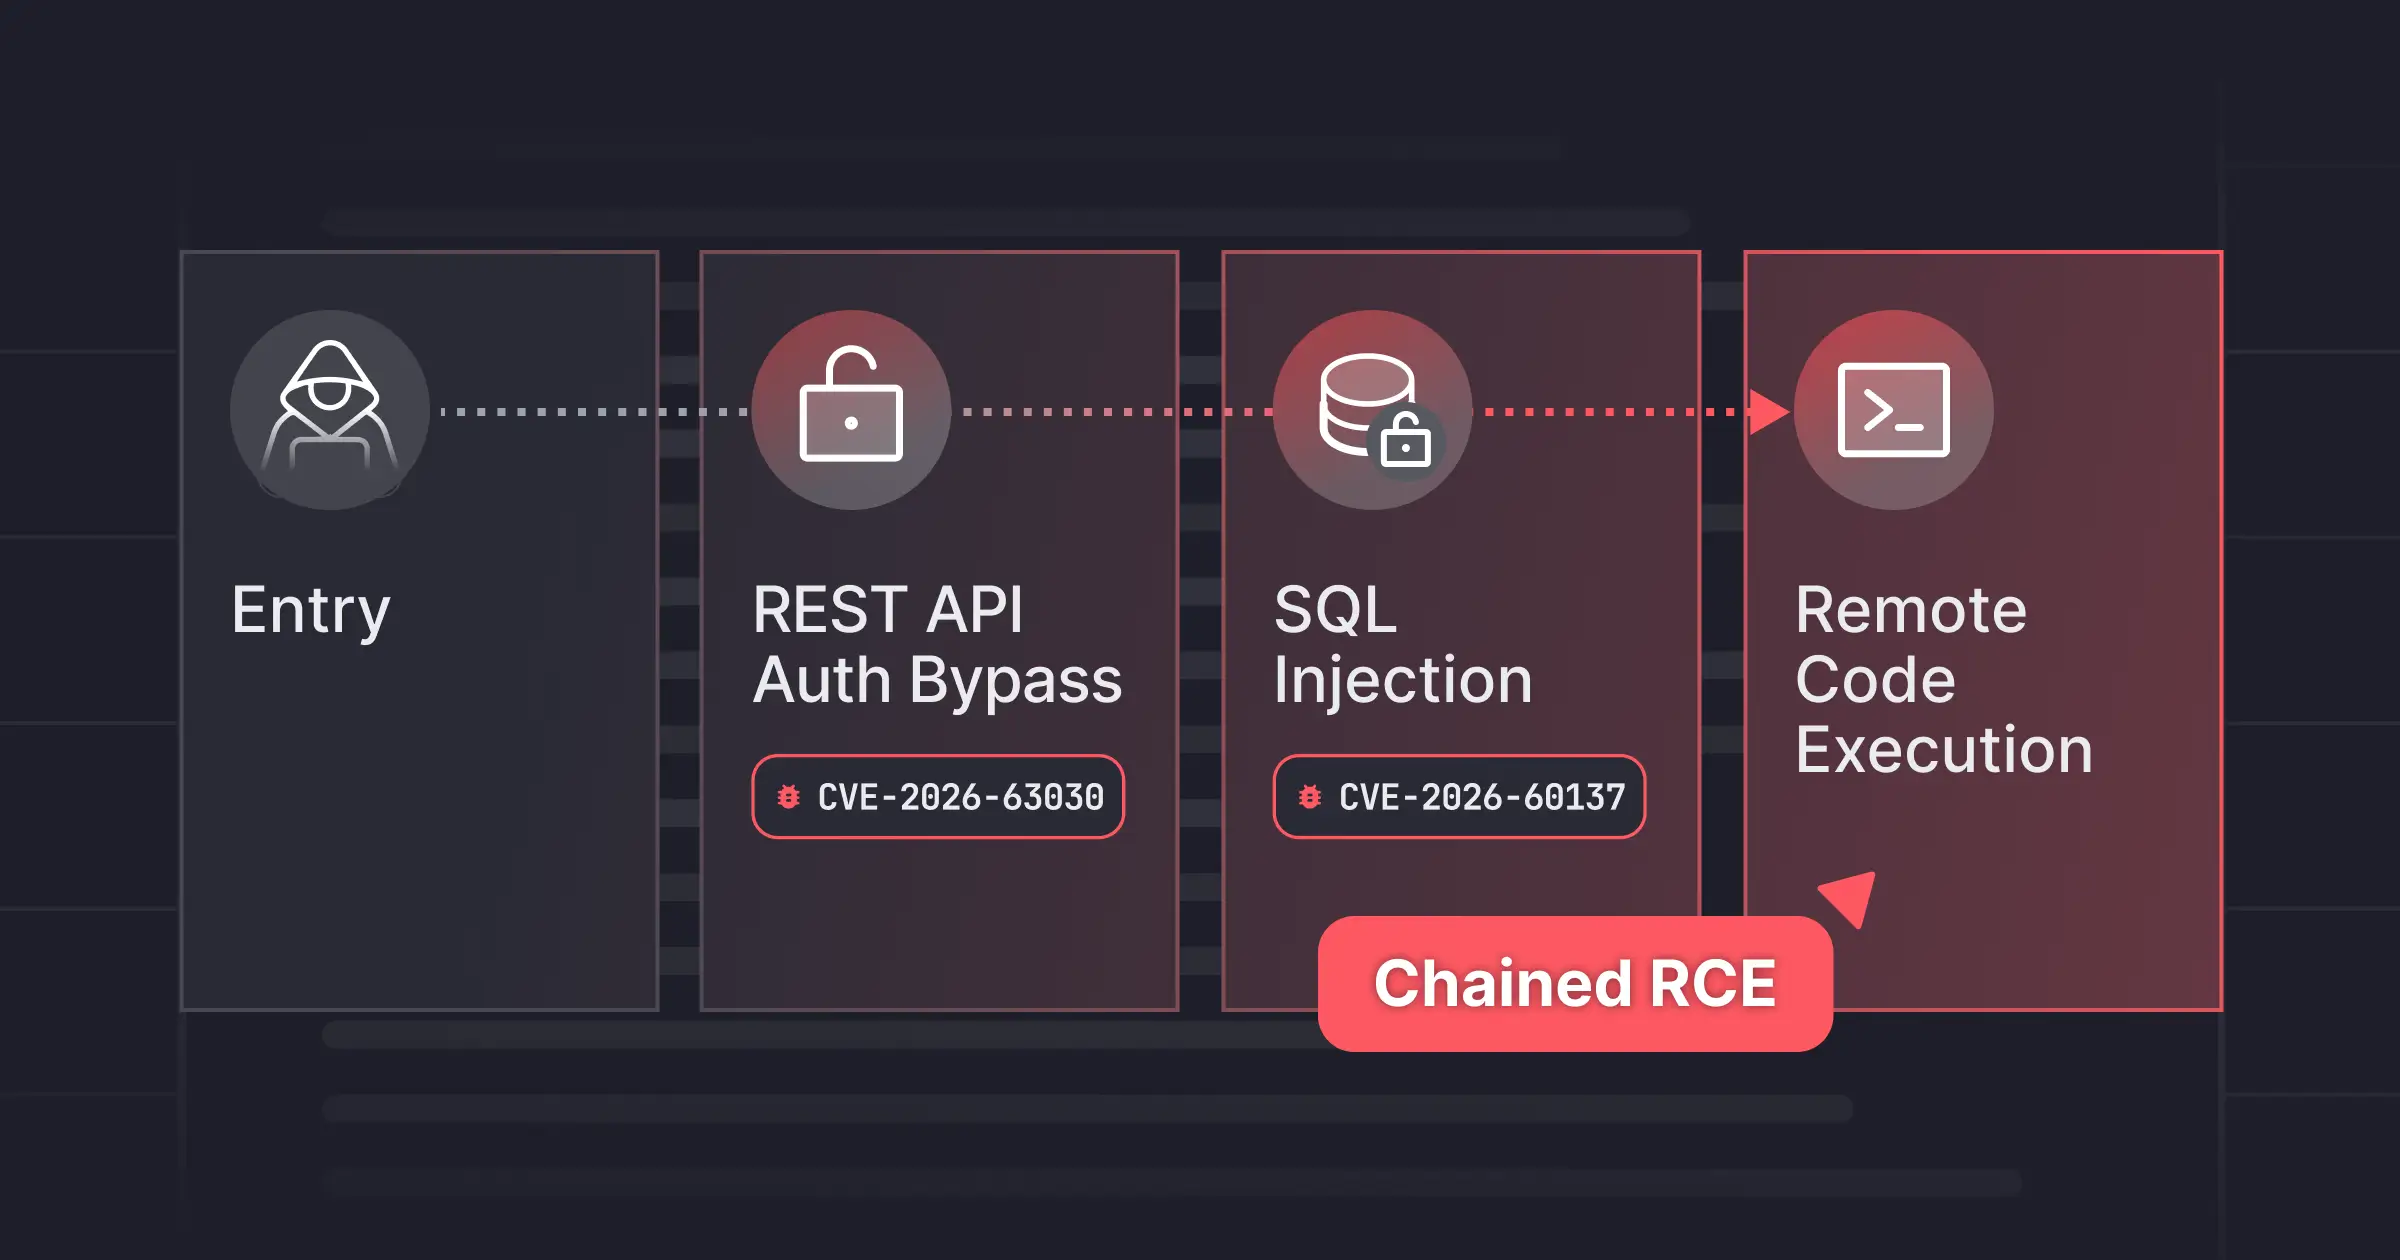
Every WordPress Site's Nightmare: Pre-Auth RCE via wp2shell
Security
Research
A stock WordPress install can be taken over by one anonymous request. Inside wp2shell: CVE-2026-60137 + CVE-2026-63030.
Read More
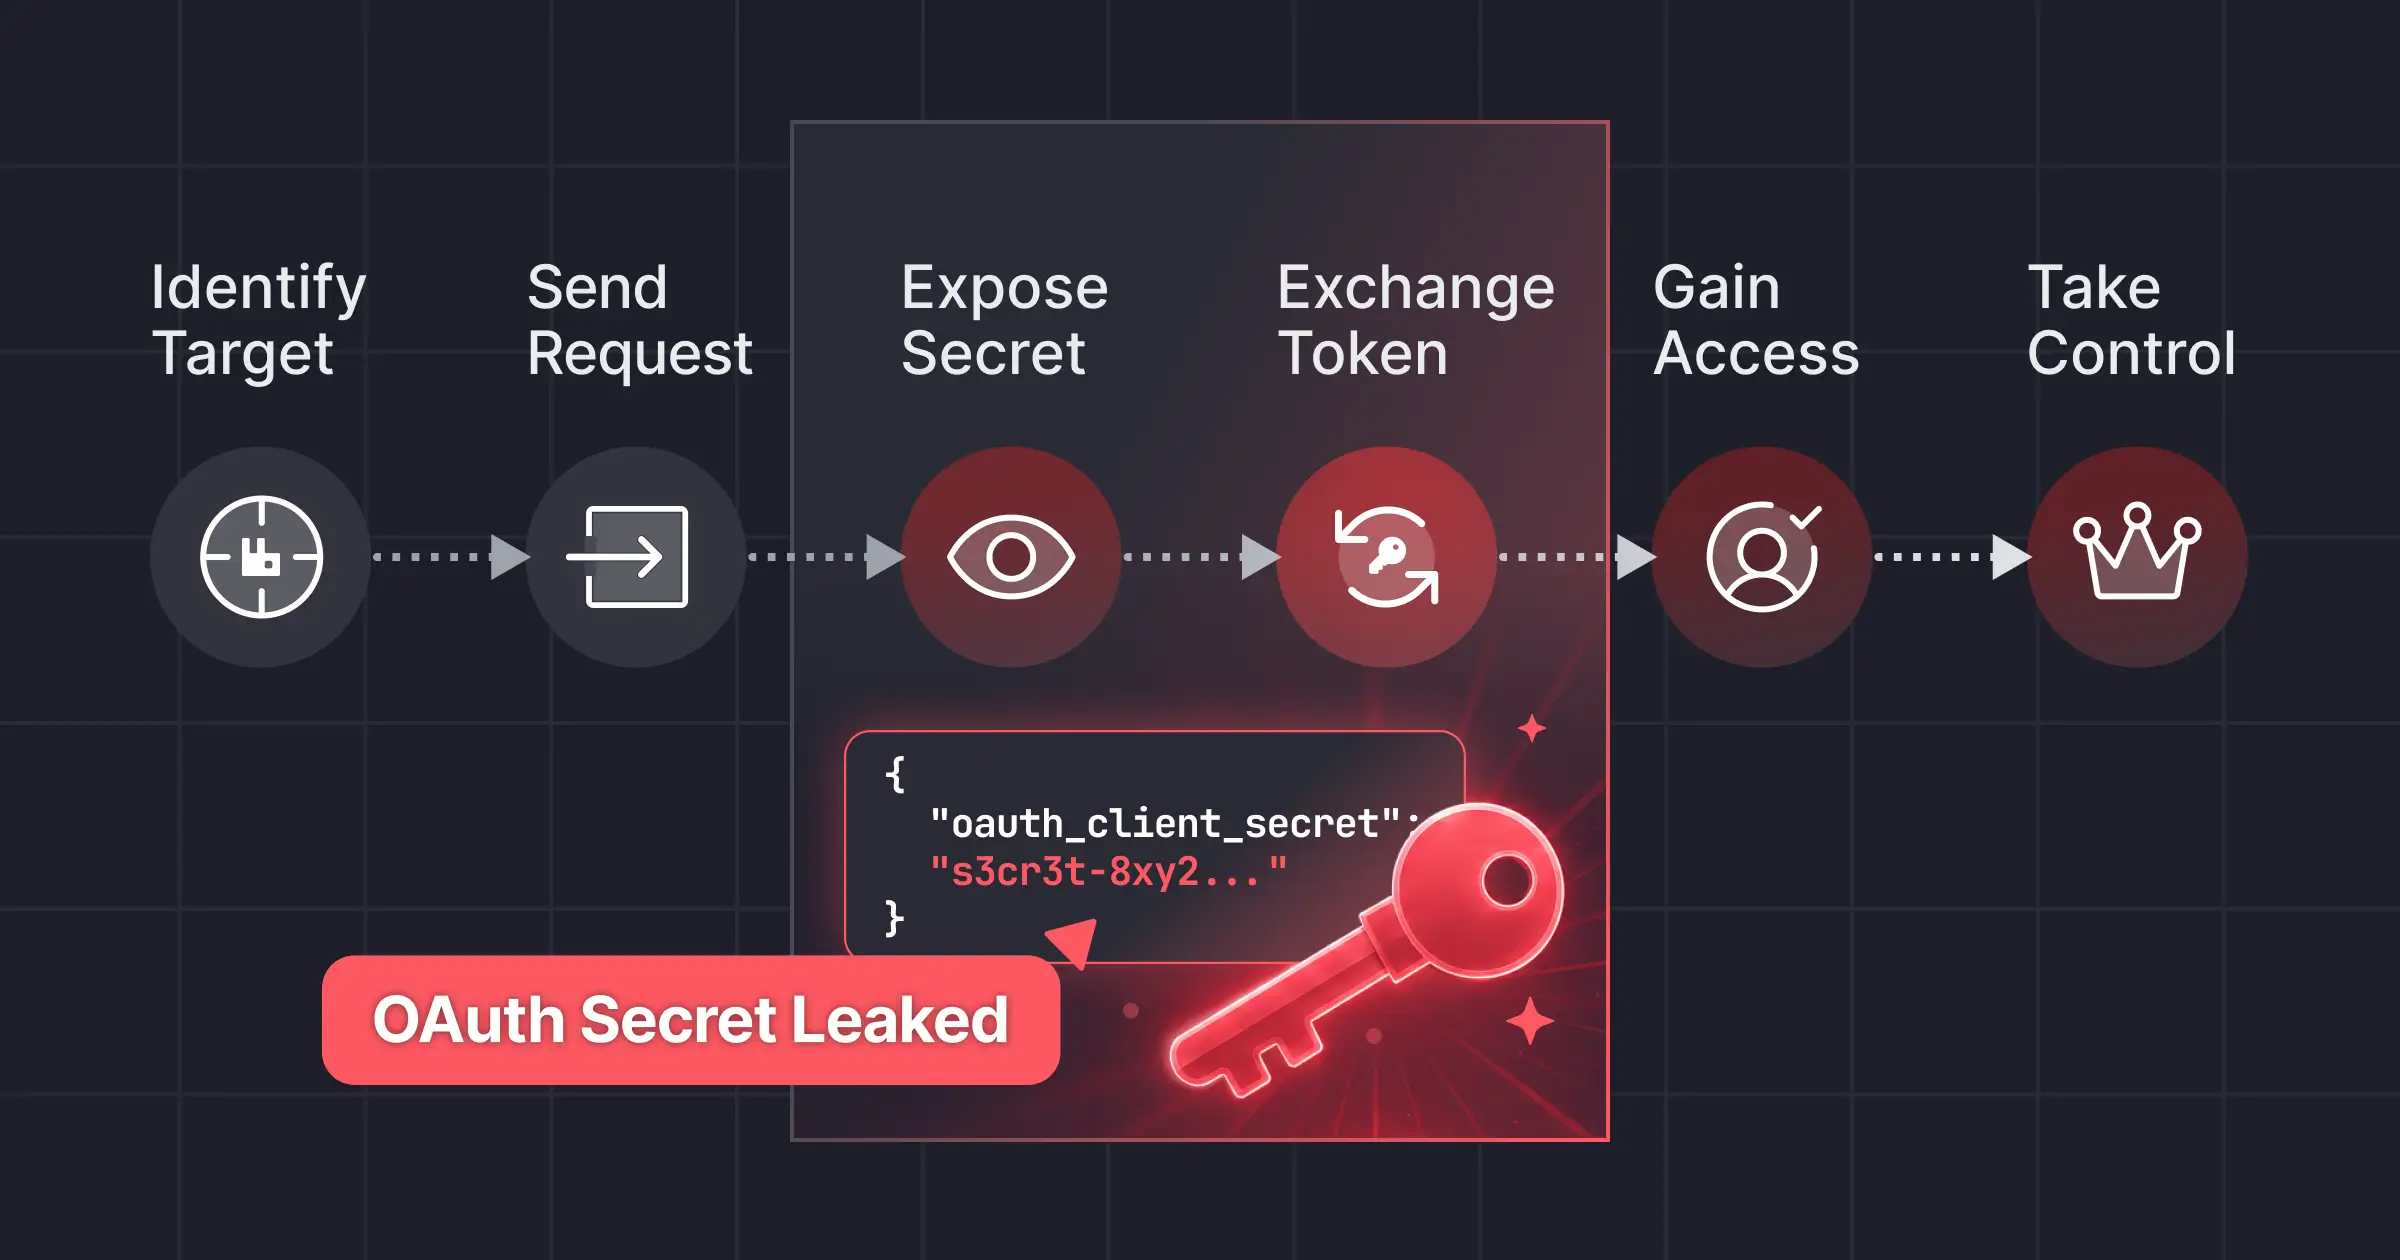
Full Broker Takeover, No Login Required: Miggo Discovers Critical RabbitMQ Vulnerabilities Putting Application Data at Risk
Security
Research
Miggo uncovered two critical RabbitMQ flaws enabling unauthenticated broker takeover and tenant data exposure. Learn who is affected.
Read More
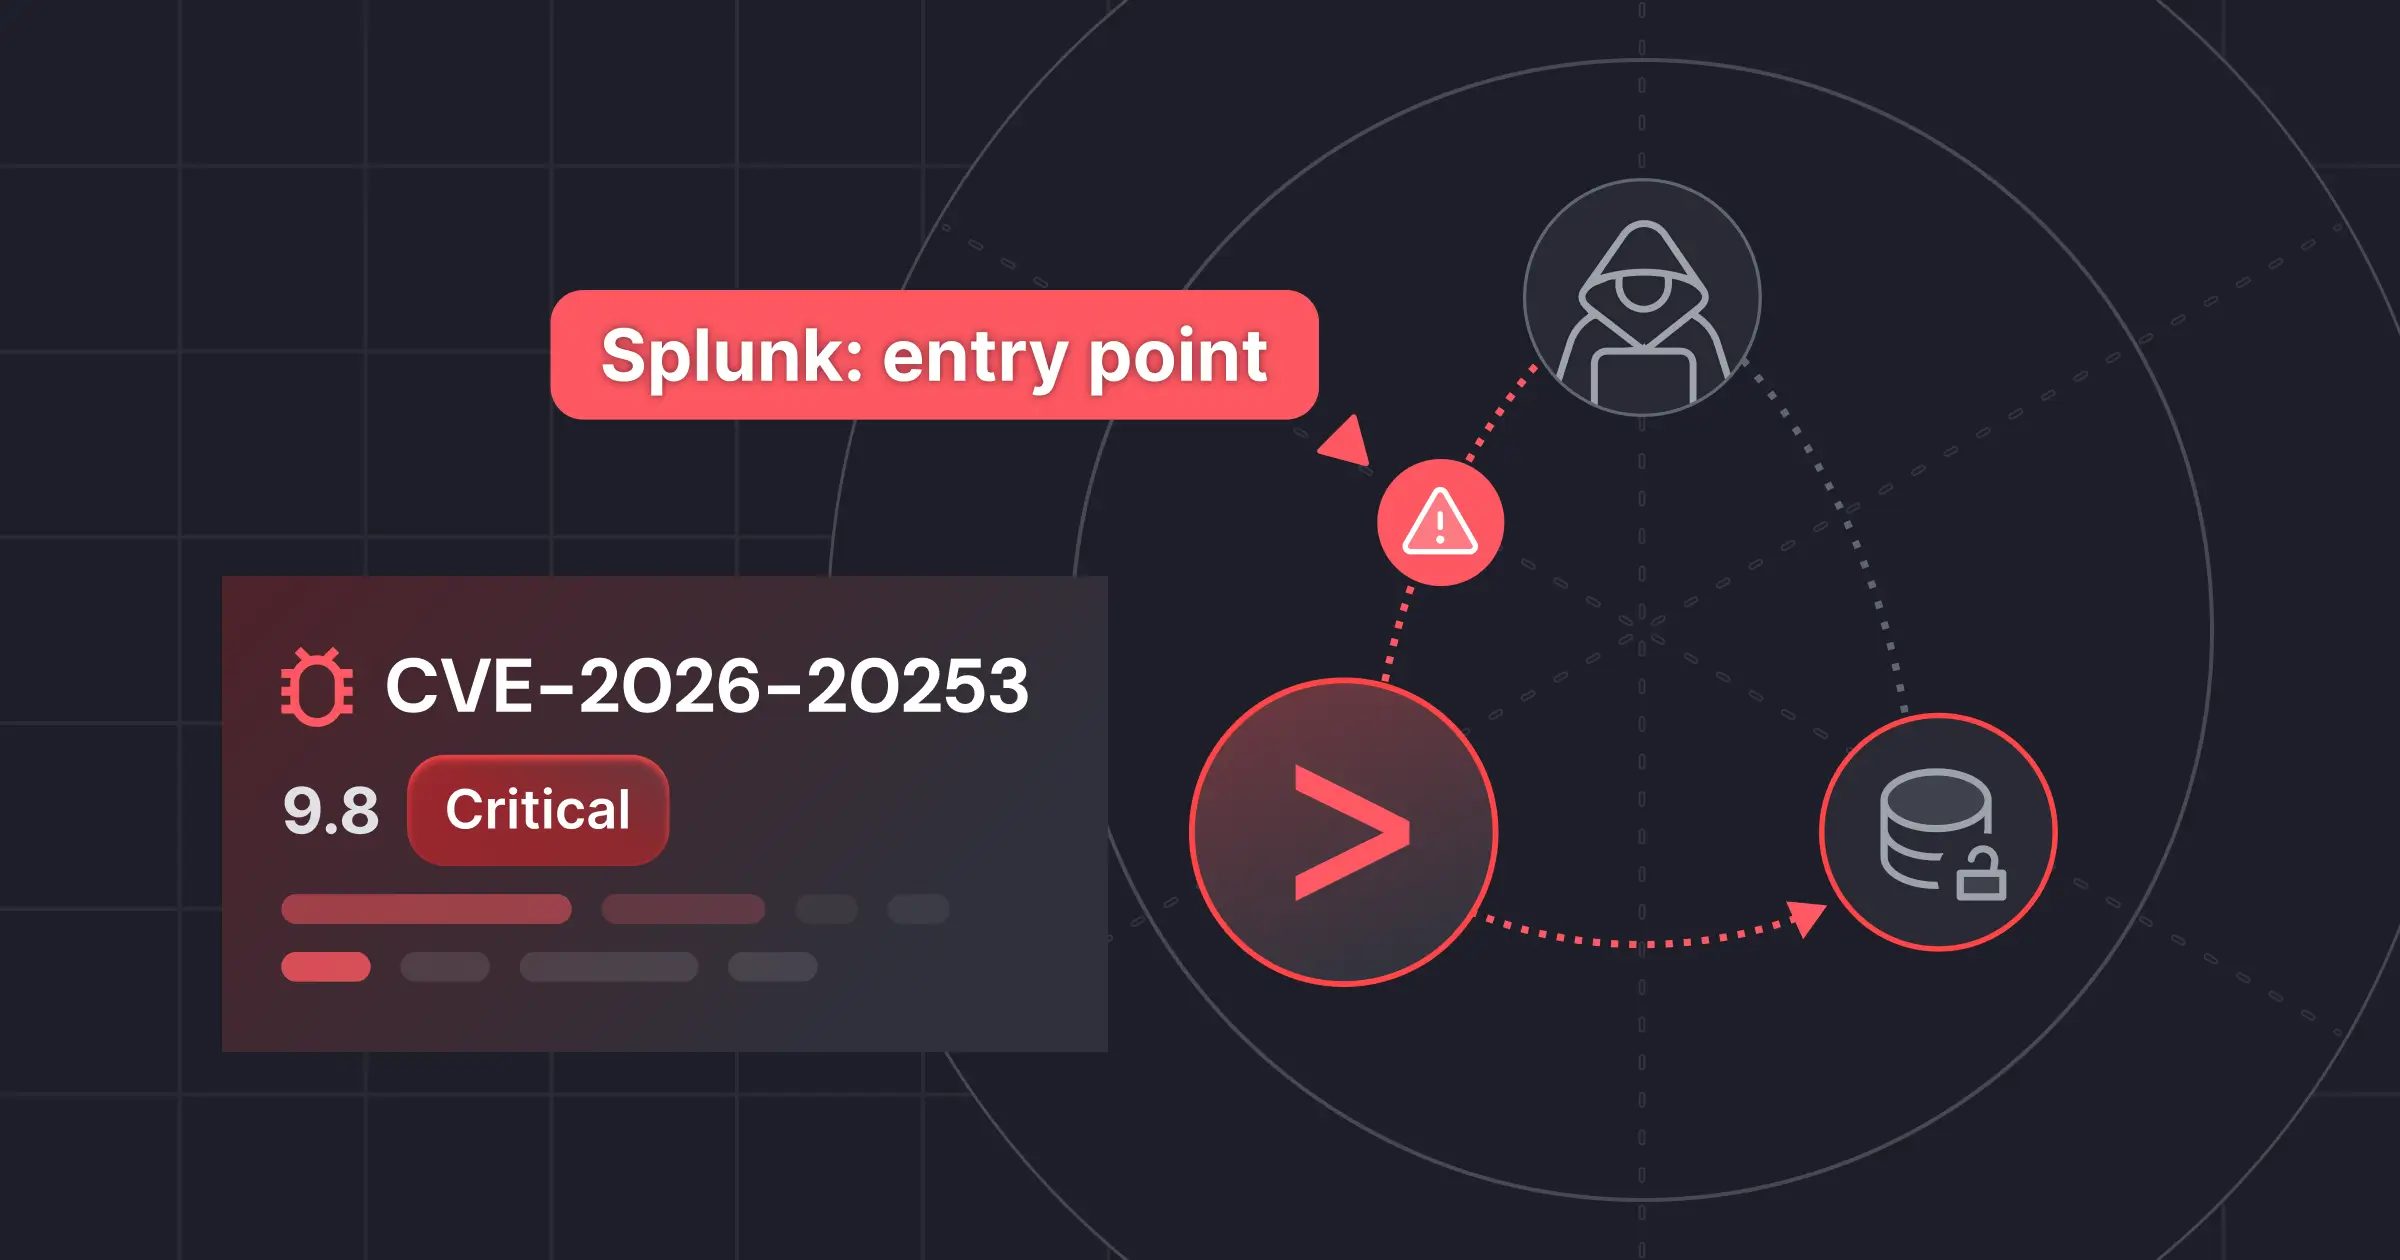
Blind the Watcher: Stopping the Unauthenticated Splunk RCE (CVE-2026-20253) Before the Patch Lands
Security
Research
CVE-2026-20253 turns Splunk Enterprise into an unauthenticated way in. Learn how the exploit works and how Miggo blocks it.
Read More
The Security Patch that Created a Vulnerability: Miggo Security Releases Detector for CVE-2026-23111 to Catch an Attack Before a Fix
Research
Security
A Linux vulnerability introduced by a security fix remained exposed for 2.5 years. Miggo built the first working exploit and detection.
Read More
BOD 26-04 Ended CVSS. How Runtime Mitigation Achieves SSVC Compliance and More
Product
CISA's BOD 26-04 shifts vulnerability prioritization beyond CVSS. Learn how Miggo operationalizes SSVC with runtime context.
Read More
95 Minutes: What Grafana's Response to a Critical RCE Says About the Future of Vulnerability Management
Security
Research
Critical Grafana RCE patched in 95 minutes — and what that response reveals about modern vulnerability management.
Read More
80% of Organizations that Miss the 24-Hour Patch Window Are Breached by Known Vulnerabilities
Security
Research
New CSA and Miggo research reveals why known vulnerabilities still cause breaches and why runtime security is becoming a top investment priority.
Read More
The Death of "Patch First": Exploiting and Mitigating Drupal CVE-2026-9082 under 60 Minutes
Security
Research
We built a working exploit for Drupal CVE-2026-9082 in under an hour. Here’s what that means for modern disclosure.
Read More
From CVE to WAF Rule in Minutes: What We Learned Building an AI Pipeline that Ships
Security
Research
AI-generated WAF rules fail without exploit testing, FP validation, and platform optimization. Here's how Miggo built its pipeline.
Read More
Two LPEs in One Week: Why Runtime Detection Matters More Than Ever
Security
Research
Two rare Linux LPEs surfaced within a week, highlighting why runtime detection matters more than ever.
Read More
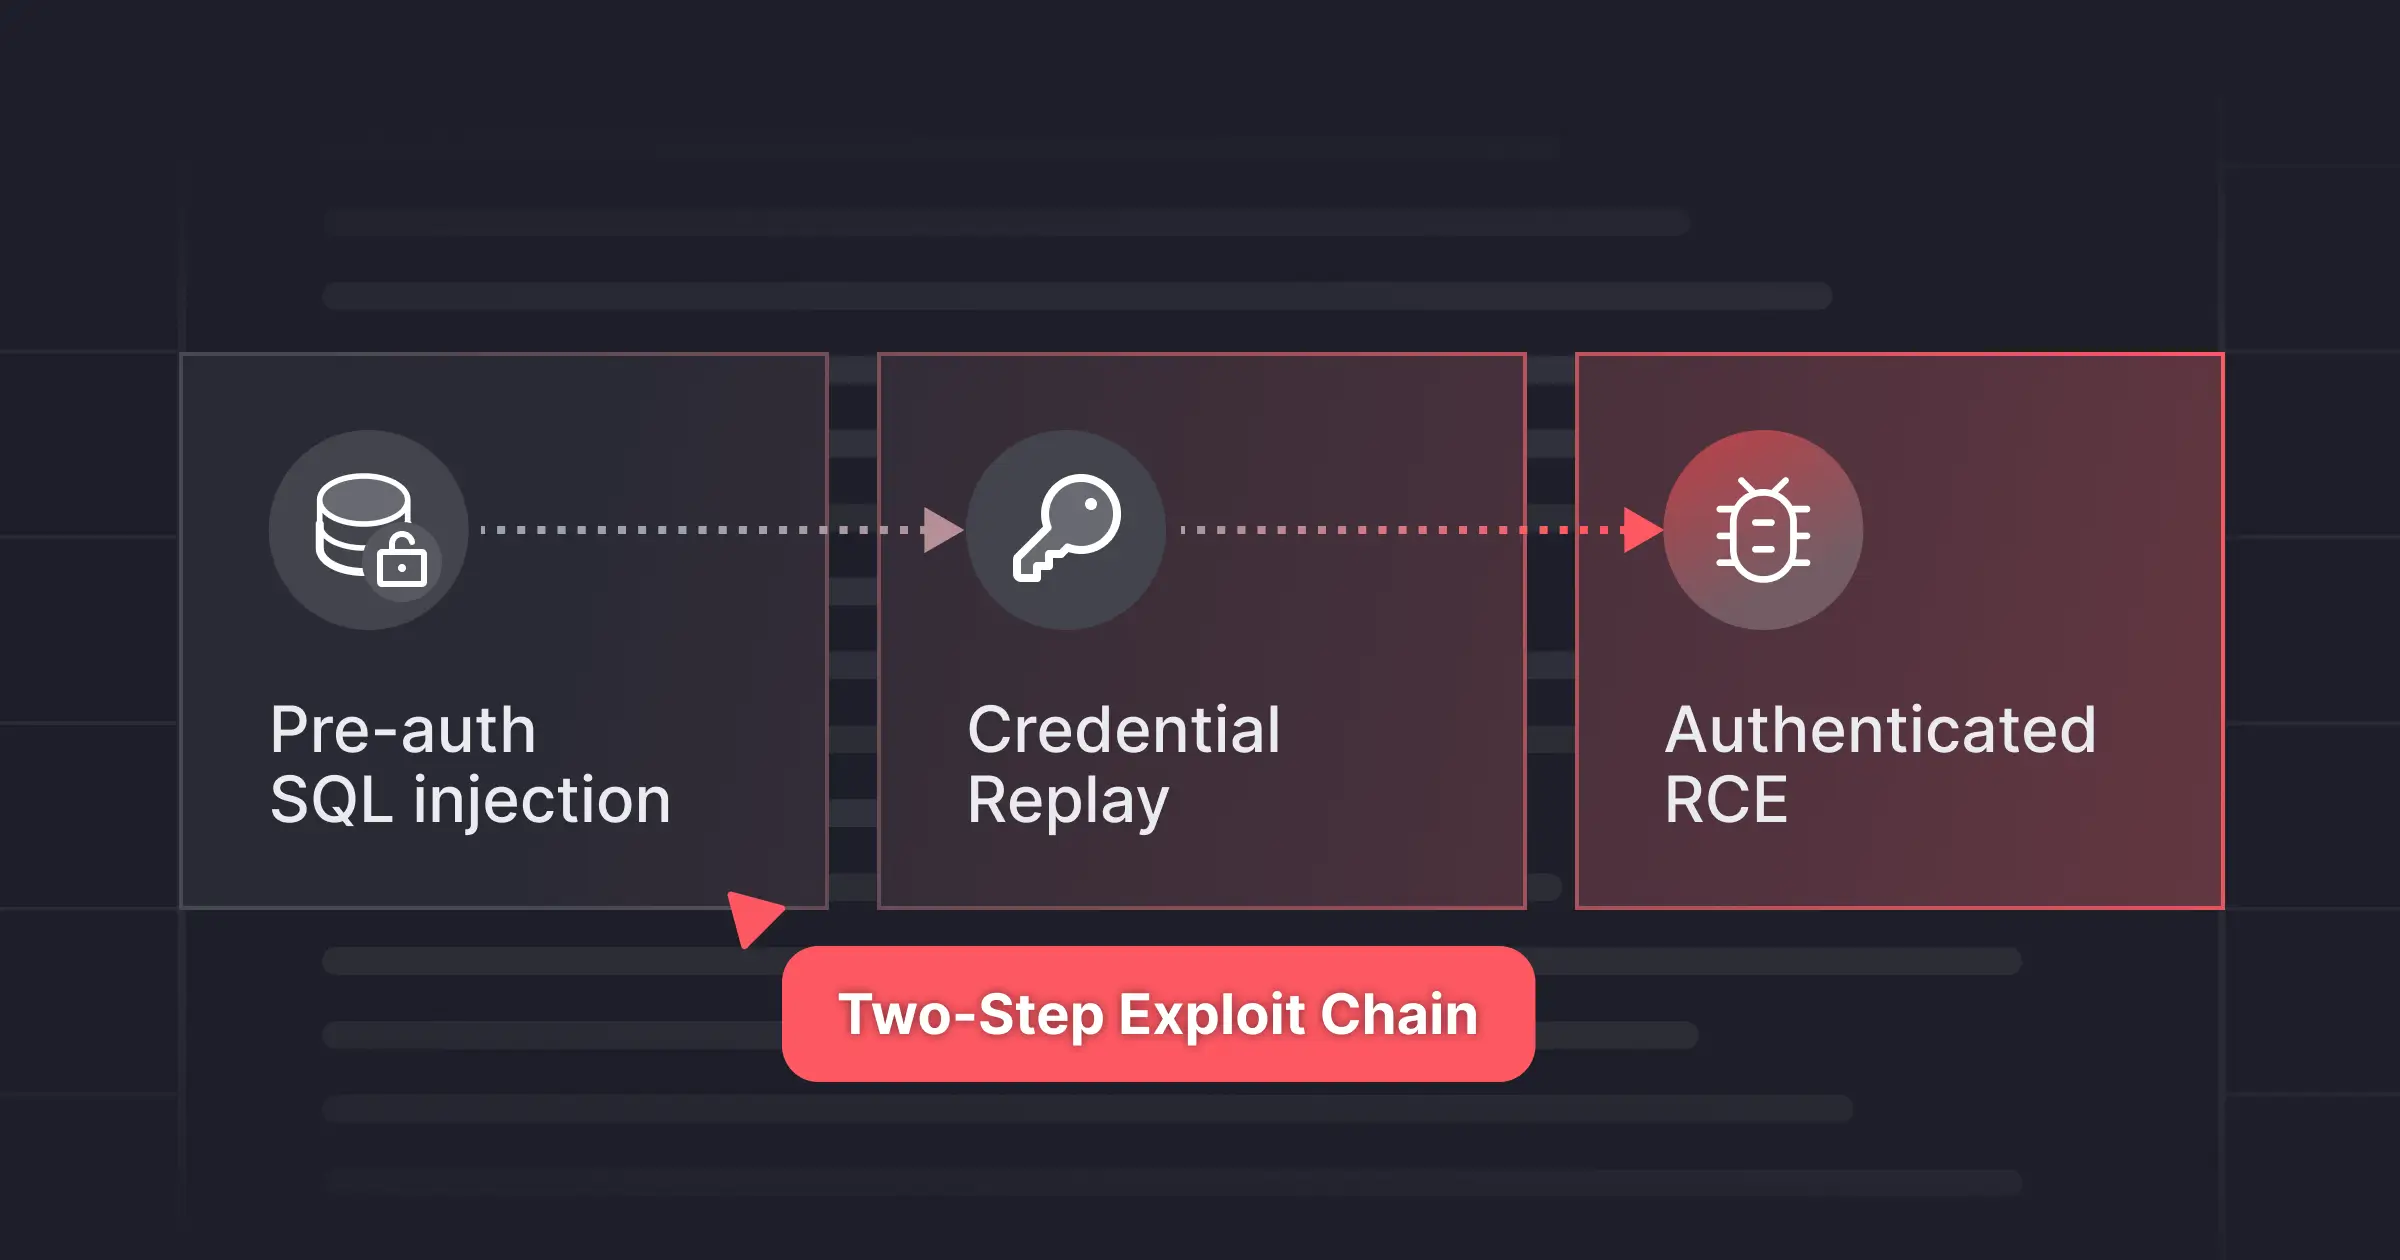
RCE in LiteLLM (CVE-2026-42208): How Two Vulnerabilities and 36 Hours Turn an AI Gateway into a Backdoor
Security
Research
Pre-auth SQLi in LiteLLM enables key theft and RCE in two requests—Miggo detects and blocks the exploit end-to-end.
Read More
Miggo Security Launches Miggo Pulse: The First End-to-End Defense Against AI-Accelerated Exploitation
Product
Miggo launches Pulse, the first end-to-end solution to detect, validate, and stop AI-accelerated threats in minutes.